BrokerOS · Section
Compliance
A control that runs after the fact tells you about a problem you already have. Every capability here sits in the path — screening before money moves, rules enforced at signup, decisions recorded as they are made.
See it live
Five controls, one compliance layer
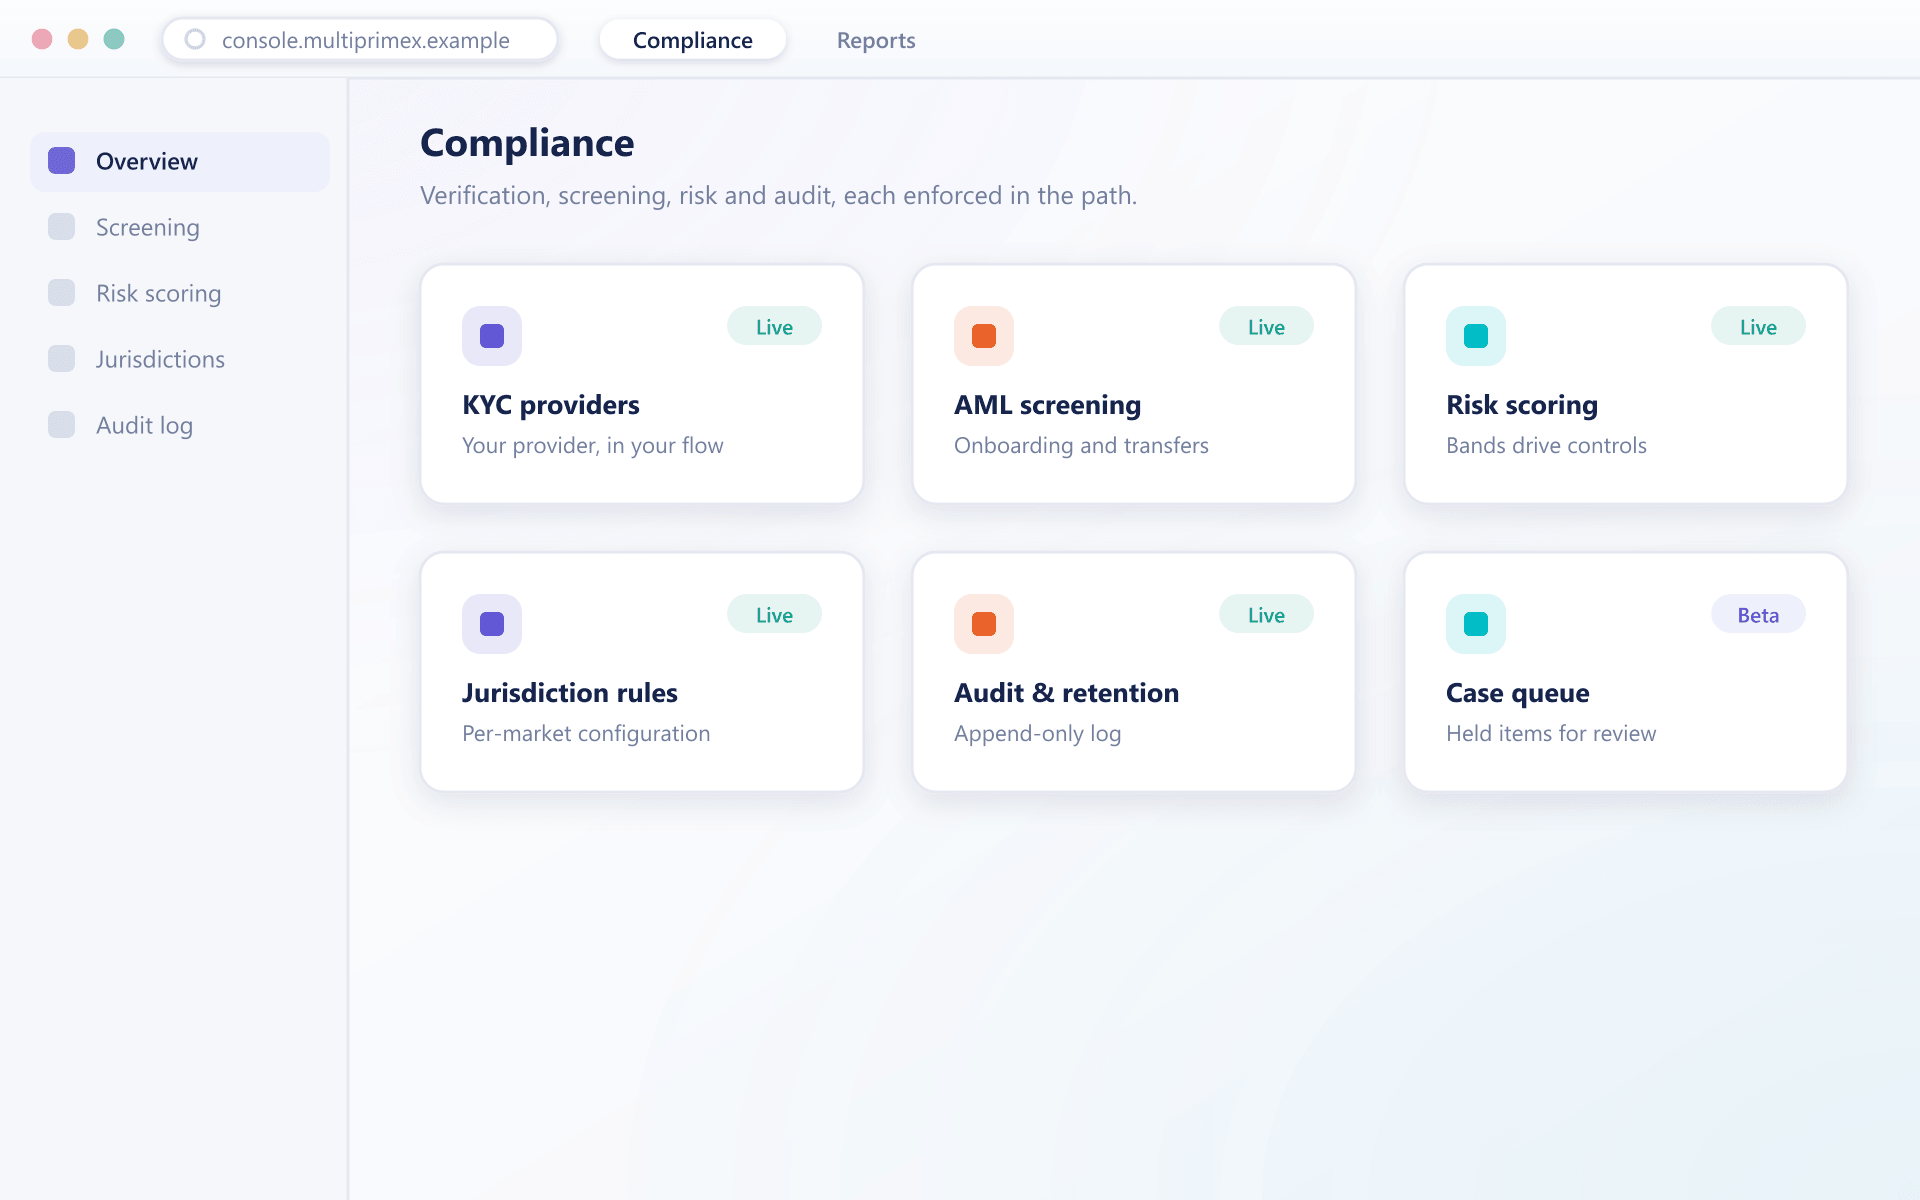
Verification, screening, risk scoring, jurisdiction rules and audit sit behind one navigation, each enforced by the platform rather than documented separately.
What it covers
The controls a regulator will ask you to evidence
Verification, screening, risk and retention are configured against the licences you hold rather than applied uniformly to everyone.
Your verification providers, swappable
Identity providers sit behind one onboarding flow, so changing provider does not mean rebuilding the client journey or retraining your desk.
Screening at the moments that matter
Sanctions and politically exposed person checks run at onboarding and on an ongoing basis, with hits routed to a reviewer rather than silently blocking a client.
Risk scoring you can argue with
Scores are built from inputs you can see and weight, so a reviewer understands why a client was escalated instead of trusting a number.
Rules per jurisdiction
Leverage caps, product availability, document requirements and marketing consent follow the entity and licence a client falls under.
Retention that survives an audit
Records, documents and decisions are retained for the period your regime requires and exported in formats an auditor will accept.
Compliance questions
What you keep control of
5 short answers to what teams ask before a demo.
No. Bring the provider you already have a contract with. It connects through the same integration layer and is routed by the same rules as any other.
Yes. Each entity and jurisdiction carries its own verification requirements, limits and product availability, and a client is mapped to one of them at onboarding.
It goes to a reviewer with the match detail attached rather than blocking the client outright, so a false positive does not cost you an account.
For the period you configure, which should follow your regime rather than ours. Retention is set per record type and enforced automatically.
Yes. The audit trail records the person, the time, the source and the state before and after, and it is queryable and exportable.
Still have a question?
A specialist will answer it directly, with your set-up in mind.
Ask a specialistBring your compliance team to the walkthrough
We will hold a transfer at screening, show what a risk band actually enforces, and answer a real question from the audit log.