Platform Essentials
Traders who write code should not have to email support
Programmatic trading breaks down at the credential step more often than at the code. Traders issue and scope their own API tokens from inside the terminal, and you keep the limits.
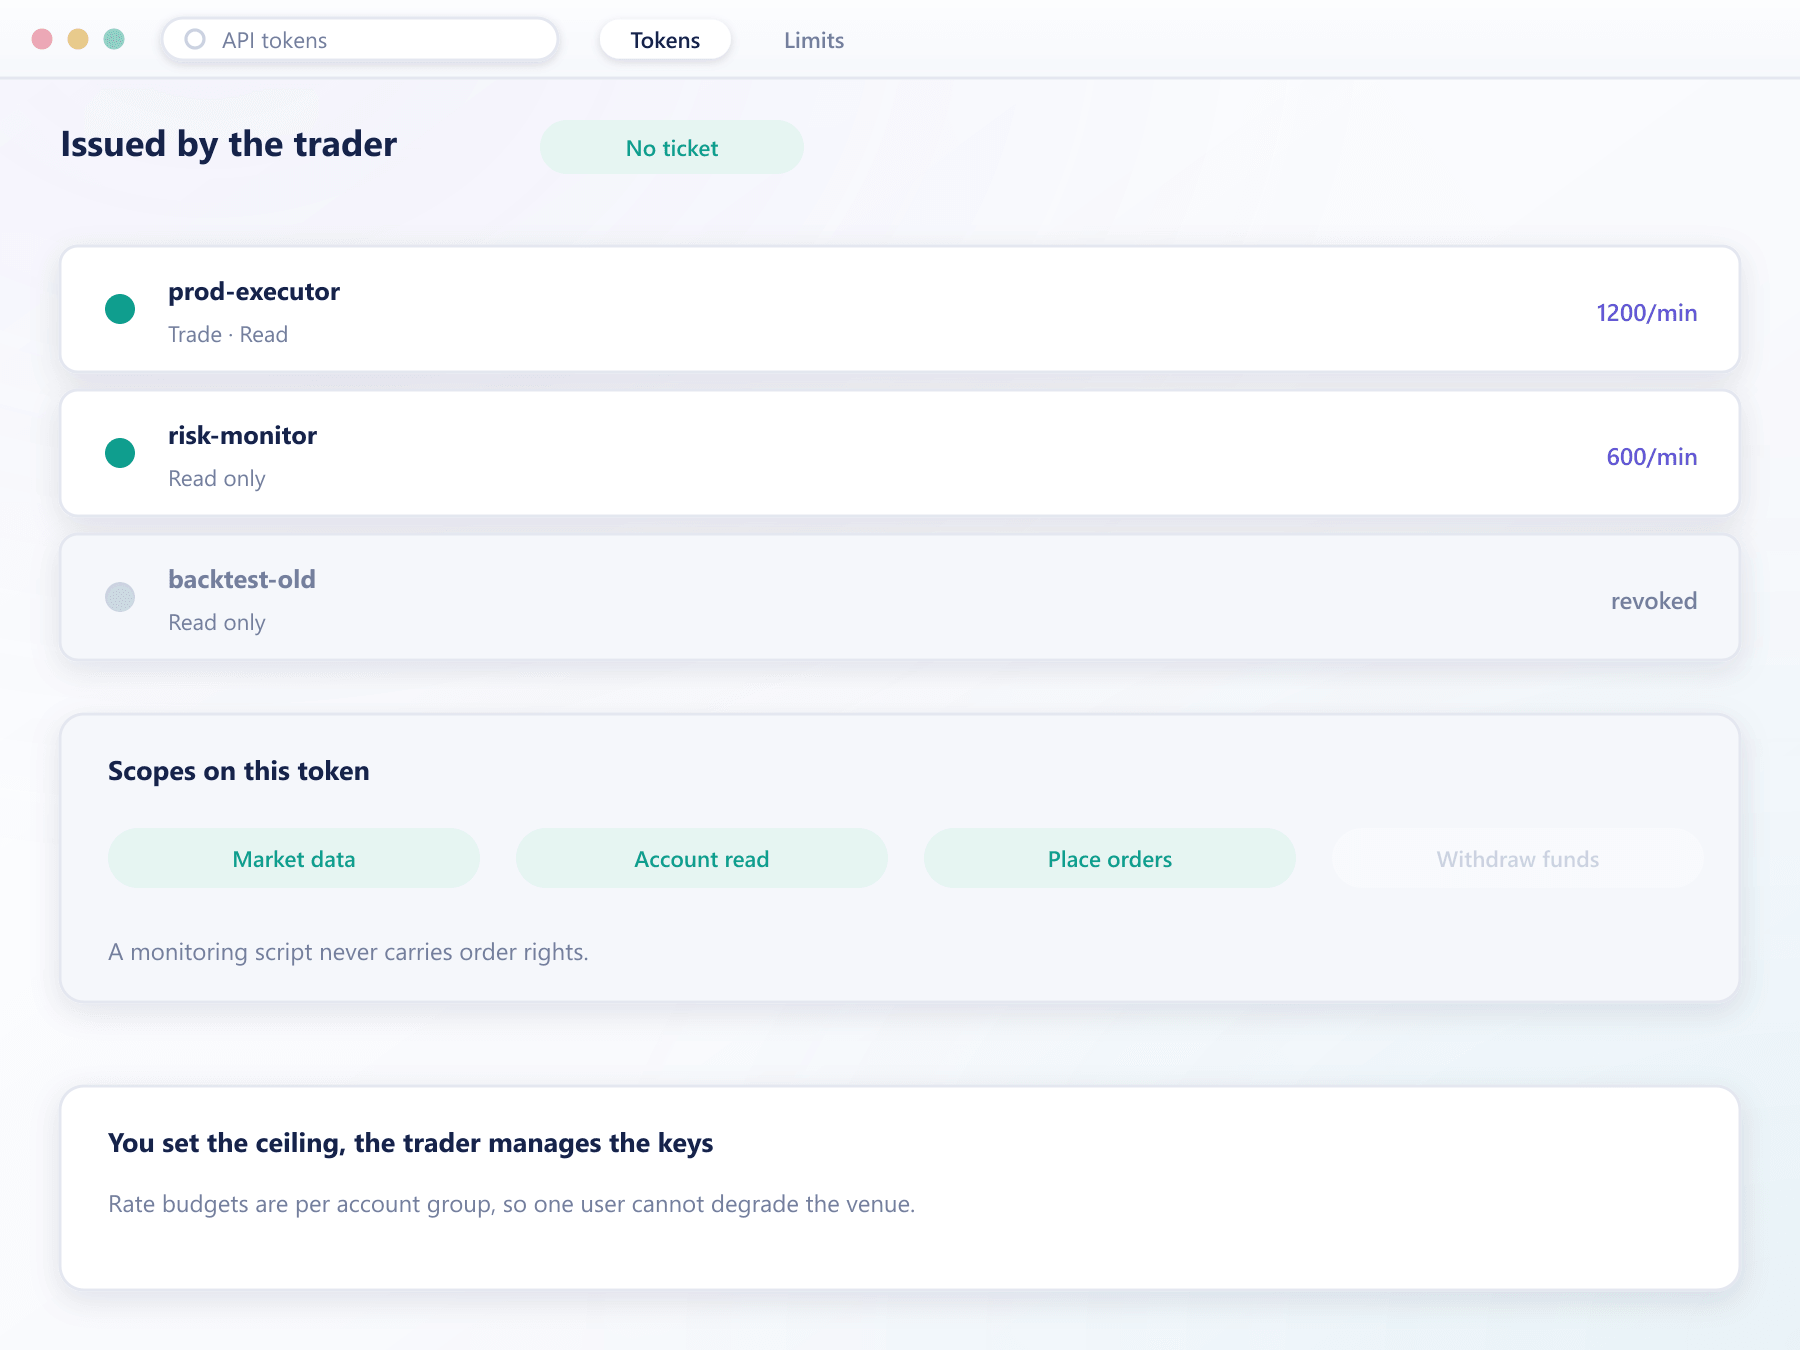
What a trader controls
Self-serve credentials, bounded by your rules
Issuing access is the trader's job. Deciding how much access exists is yours.
Tokens issued in the terminal
A trader creates, names and revokes their own keys without raising a ticket, which removes the slowest step in getting an algorithm live.
Scopes per token
Read-only market data, account read, or full trading are separate permissions, so a monitoring script never carries order rights.
Rate limits by tier
Request budgets are set per account group, so a heavy user cannot degrade the venue for everyone else.
REST and streaming both
Order entry and account queries over REST, market data and fills over a persistent stream, without running two integrations.
Every call attributed
Activity is recorded against the token that made it, so unusual behaviour can be traced to a credential rather than an account.
How it runs
From key to live algorithm
Create a token
The trader names it, picks its scopes and copies the secret once. It is never shown again.
Build against the sandbox
The same interface with test balances, so a strategy is debugged before it touches a funded account.
Go live within the limits
Rate budgets and scopes follow the token into production without a separate promotion step.
You keep visibility
Which accounts run automated flow, at what rate, and against which endpoints is visible in the broker console.
API questions
What automated access allows
4 short answers to what teams ask before a demo.
Yes, and that is deliberate. You set what a token can do and how fast it can call; within that, a trader manages their own credentials.
Yes. Tokens are revoked individually, so a leaked key does not mean locking a client out of the terminal.
Requests are refused with a clear response rather than silently dropped, and the limit is per group so one account cannot affect another.
No. Order entry runs over REST and market data over a persistent stream, but both sit behind the same credential and the same documentation.
Still have a question?
A specialist will answer it directly, with your set-up in mind.
Ask a specialistPut your engineers in front of the API
Sandbox credentials and the reference come before any commercial conversation, because that is how this gets evaluated properly.